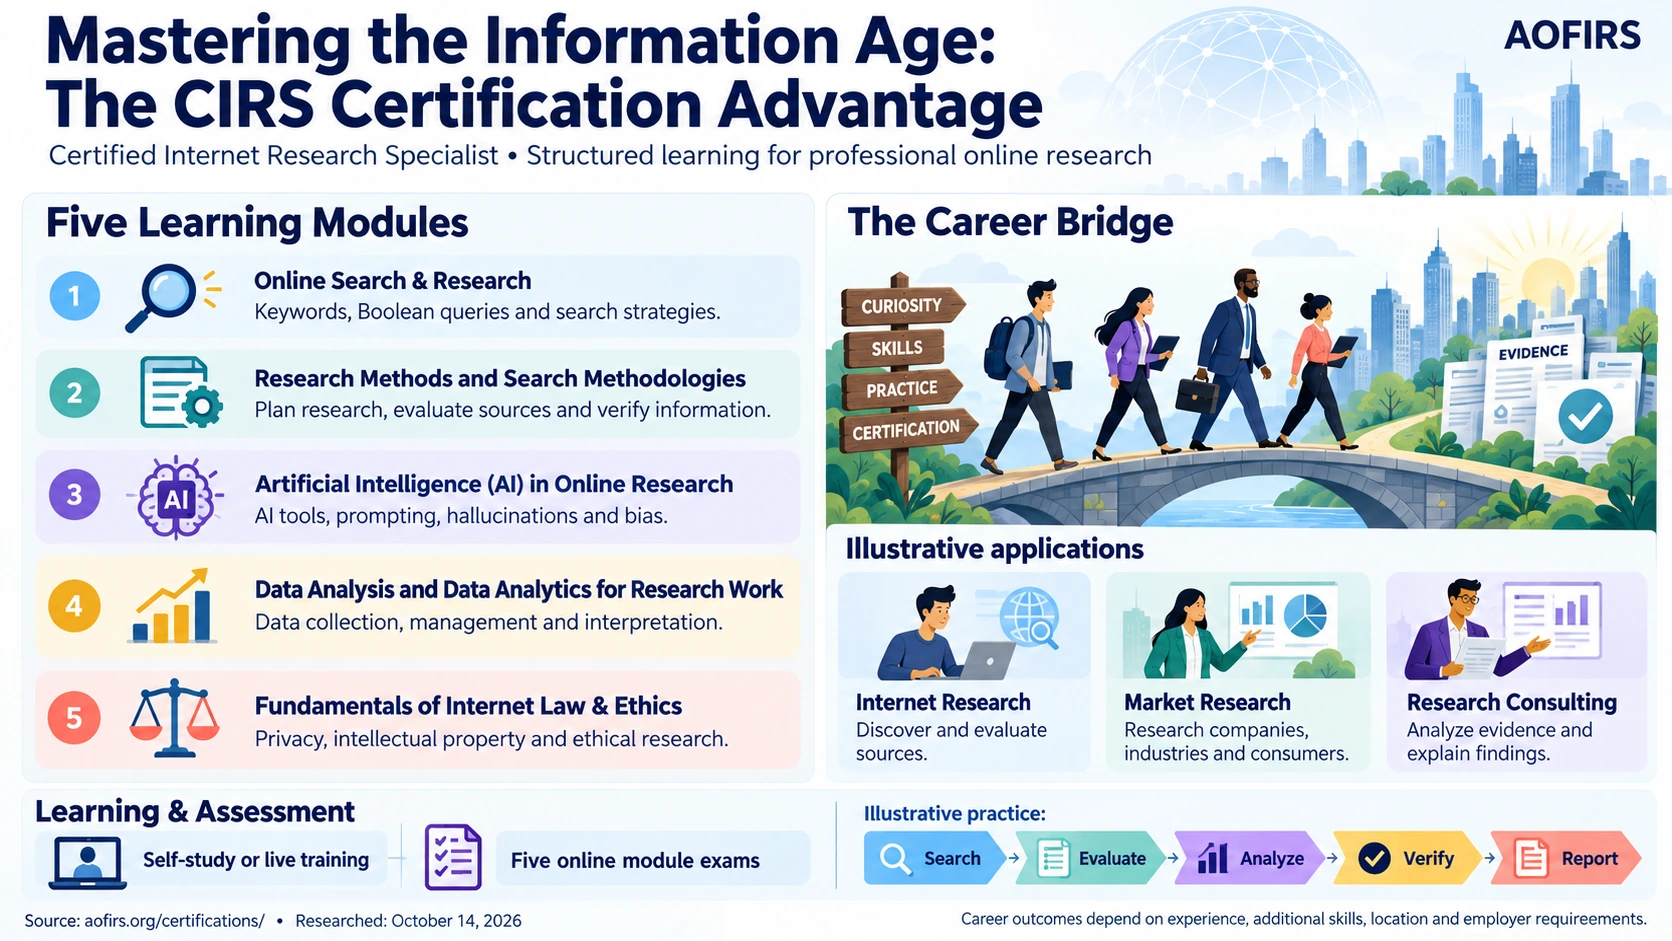
In 2026, a convincing email proves nothing. Large language models now draft more than half of all spam, producing grammatically flawless lures that slip past content filters. Attackers can’t fabricate as easily the mechanical record every mail server stamps on a message in transit. Email header forensics reads that record—routing hops, envelope data, and cryptographic signatures—to establish where a message really came from and whether it can be trusted.
Interactive Presentation: Modern Email Forensics
Learn more: read the research report How To Verify Your Email and Prevent Fraud, and the CIRS™ program.
Why Headers Beat Prose: AI Offense vs. Forensic Defense
Generative AI has removed the classic telltale signs of phishing—spelling errors, awkward phrasing, generic greetings. Content can be fabricated in seconds; server routing cannot. Each Mail Transfer Agent (MTA) leaves structural fingerprints that remain durable evidence of fraud. As a complementary countermeasure, stylometric detection compares a message’s statistical fingerprint against a sender’s known-good baseline to flag AI-hijacked threads.
The Journey of an Email
1. Origin
The sender hits send in a Mail User Agent (MUA), handing off the payload.
2. Transfer
Outbound mail enters a queue; the sending MTA handles every aspect of delivery.
3. Resolution
MTAs query DNS for the recipient domain’s authorized Mail Exchange (MX) servers.
4. Routing & Delivery
Each server hop adds a “postmark” (Received: line) until the message reaches the inbox.
Anatomy of a Full Header
Return-Path(envelope sender): where bounces are routed—the account that actually transmitted the message.Received:(the audit trail): added by each MTA with a message ID, timestamp and the true identity of the sending server.Authentication-Results: the receiving server’s SPF, DKIM and DMARC verdicts.X-Spam-Status: spam score versus the required threshold, with test flags such asBAYES_56orOPT_OUT.
The Sender Identity Gap: Where Business Email Compromise Hides
| Field | Visibility | Forensic meaning | Attack pattern |
|---|---|---|---|
| Envelope sender (Return-Path) | Hidden | Actual transmitting account | attacker-controlled@freemail.com |
| From: | Visible in inbox | Easily forged display identity | CEO <ceo@trusted-company.com> |
| Reply-To: | Visible on reply | Where responses are routed | Freemail address the attacker monitors |
Alias vs. Mask
A legitimate alias (privacy, list management, branding) keeps an internally consistent Received chain with matching SPF/DKIM passes. A malicious mask shows a Return-Path unrelated to the displayed name and a server lying about its identity—producing authentication failures.
Hop-by-Hop Reconstruction: Read Bottom-Up
- Locate the origin: the bottom-most public IP (often
X-Originating-IP) is the first injection point into the internet. - Walk the chain upward: check that each claimed hostname resolves to its IP; a mismatch reveals the forgery point.
- Apply the rule of exclusion: ignore private ranges
10.x,172.16.xand192.168.x—they cannot be traced outward.
The Mandatory 2026 Authentication Stack
SPF
Lists which server IPs may send for a domain. A TXT record on the sending domain.
DKIM
Cryptographic signature proving the message was not altered; public key published in DNS.
DMARC
Tells receivers what to do when SPF/DKIM fail (none / quarantine / reject). Lives at _dmarc.domain.com.
BIMI
Shows a verified brand logo—only when DMARC is enforced at quarantine or reject.
The 2026 Investigation Toolkit
- Bulk & real-time verification: ZeroBounce and Clearout assign AI-predicted deliverability scores and resolve catch-all domains.
- Email finders: Hunter.io and Apollo.io combine domain search with firmographic data.
- IP geolocation: MaxMind GeoIP and IPinfo map public IPs to location, ISP and network owner.
- Skip-tracing boundaries: licensed professionals use FCRA-regulated credit-header tools; consumer alternatives have a lower accuracy ceiling.
The Limits of IP Geolocation
Coordinates describe network infrastructure, not a household. VPNs, proxies and corporate NAT degrade accuracy. Check the network-owner field: a generic commercial VPN indicates an exit node; a recognizable regional ISP block is a reliable geographic signal.
Case Study: Dissecting a Lotto Scam
A “LOTTO WINNING NOTIFICATION” arrives from Mrs Maria Cook <www@bridge.ocn.ne.jp>—a syntactically valid but machine-generated local part. The Reply-To points to an unrelated Gmail address referencing a wire-transfer service: the identity gap in action. The bottom-most X-Originating-IP, 41.86.234.171, becomes the investigative thread.
Geographic trilateration: Talos Intelligence places it in Porto-Novo, Benin (network owner ISOCEL, reputation Poor); IPTrackerOnline independently confirms the city, ISP and coordinates; Spamhaus SBL flags the range for advance-fee fraud. No single tool is proof—independent, differently-sourced databases must converge to make a finding defensible.
Defeating the $16.6B Business Email Compromise Threat
| Defense layer | Result | Why |
|---|---|---|
| 1. Content filter | Bypassed | Flawless LLM prose evades legacy detection |
| 2. Authentication | Bypassed | SPF/DKIM pass for a newly registered typosquat domain |
| 3. Identity gap | Caught | Reply-To routes to an unrelated freemail address |
| 4. IP geolocation | Caught | Origin resolves to a foreign data center, breaking the supplier’s history |
| 5. Procedural control | Final stop | Callback to an independently verified number confirms the fraud |
Video Masterclass: Trace the Origin—Verifying Suspicious Emails
The CIRS™ Investigative Discipline
Effective email verification combines human expertise (header and protocol reading), machine intelligence (AI verification software), data analysis (trilateration and network-owner extraction) and ethical practice (FCRA boundaries and licensed data tiers). The CIRS credential certifies that an investigator applies convergent evidence rather than stopping at the first plausible answer.
Become a Certified Internet Research Specialist
Master header forensics, OSINT verification and defensible reporting with the CIRS™ course package.
Frequently Asked Questions
How do I view the full header of an email?
In Gmail choose “Show original”; in Outlook open message properties; in Apple Mail use View → Message → All Headers. Copy the full text for analysis.
Which IP address shows the real sender?
Read the Received lines from the bottom up; the earliest public IP (often X-Originating-IP) is the injection point. Ignore private ranges.
If SPF and DKIM pass, is the email safe?
No. They only prove the message came from the stated domain—which may be a typosquat. Check the Reply-To, domain age and routing history too.
Can IP geolocation identify a person’s address?
No. It identifies network infrastructure and owner. VPNs and NAT can hide the true origin entirely.
What is the single best defense against BEC wire fraud?
A procedural callback to an independently verified phone number before any payment change.