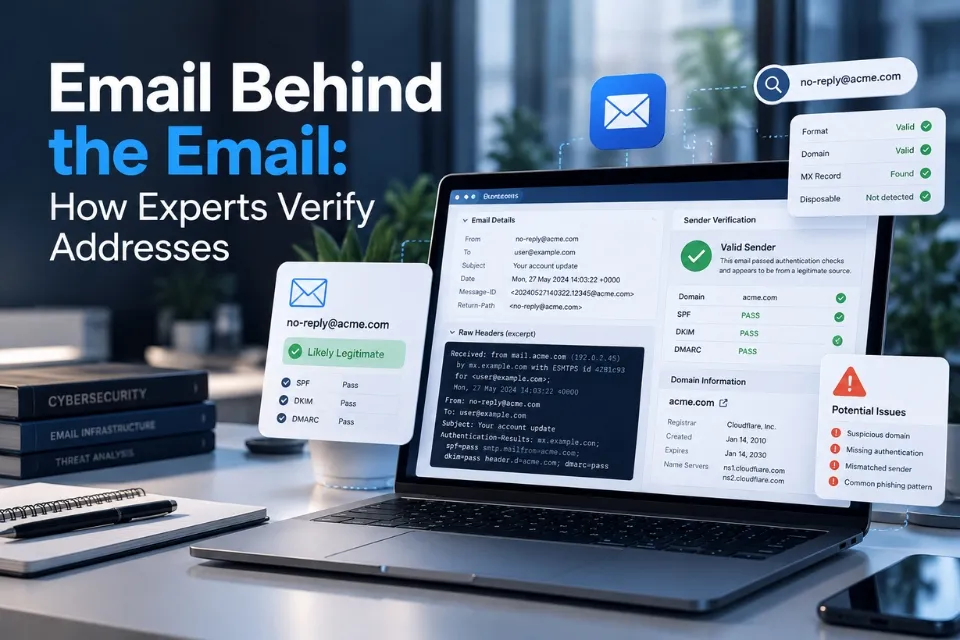
A valid email address, an authenticated domain and a verified person are three different findings. To investigate a suspicious message, preserve the original email, examine headers added by trusted receiving systems, interpret SPF, DKIM and DMARC correctly, and confirm important requests through an independently established channel.
The visible message tells you what someone wants you to believe. The technical record can show how the message was handled. Neither layer should be treated as complete proof of who pressed Send.
Quick Answer: How Experts Verify an Email Address
First define the question: can the address receive mail, did the message authenticate, or is it connected to the claimed person? Then collect evidence appropriate to that question. A deliverability score cannot answer an identity question, and an authentication pass cannot establish that a payment request is genuine.
For an urgent or sensitive request: pause the requested action and contact the organisation using a number or channel you already trust. Do not use contact details supplied only in the suspicious message.
Editorial review: 10 October 2026. Technical explanations checked against primary protocol documentation. The older CIRS case below is retained as a historical teaching example, not a fresh reputation or geolocation lookup.
Four Questions Hidden Inside “Email Verification”
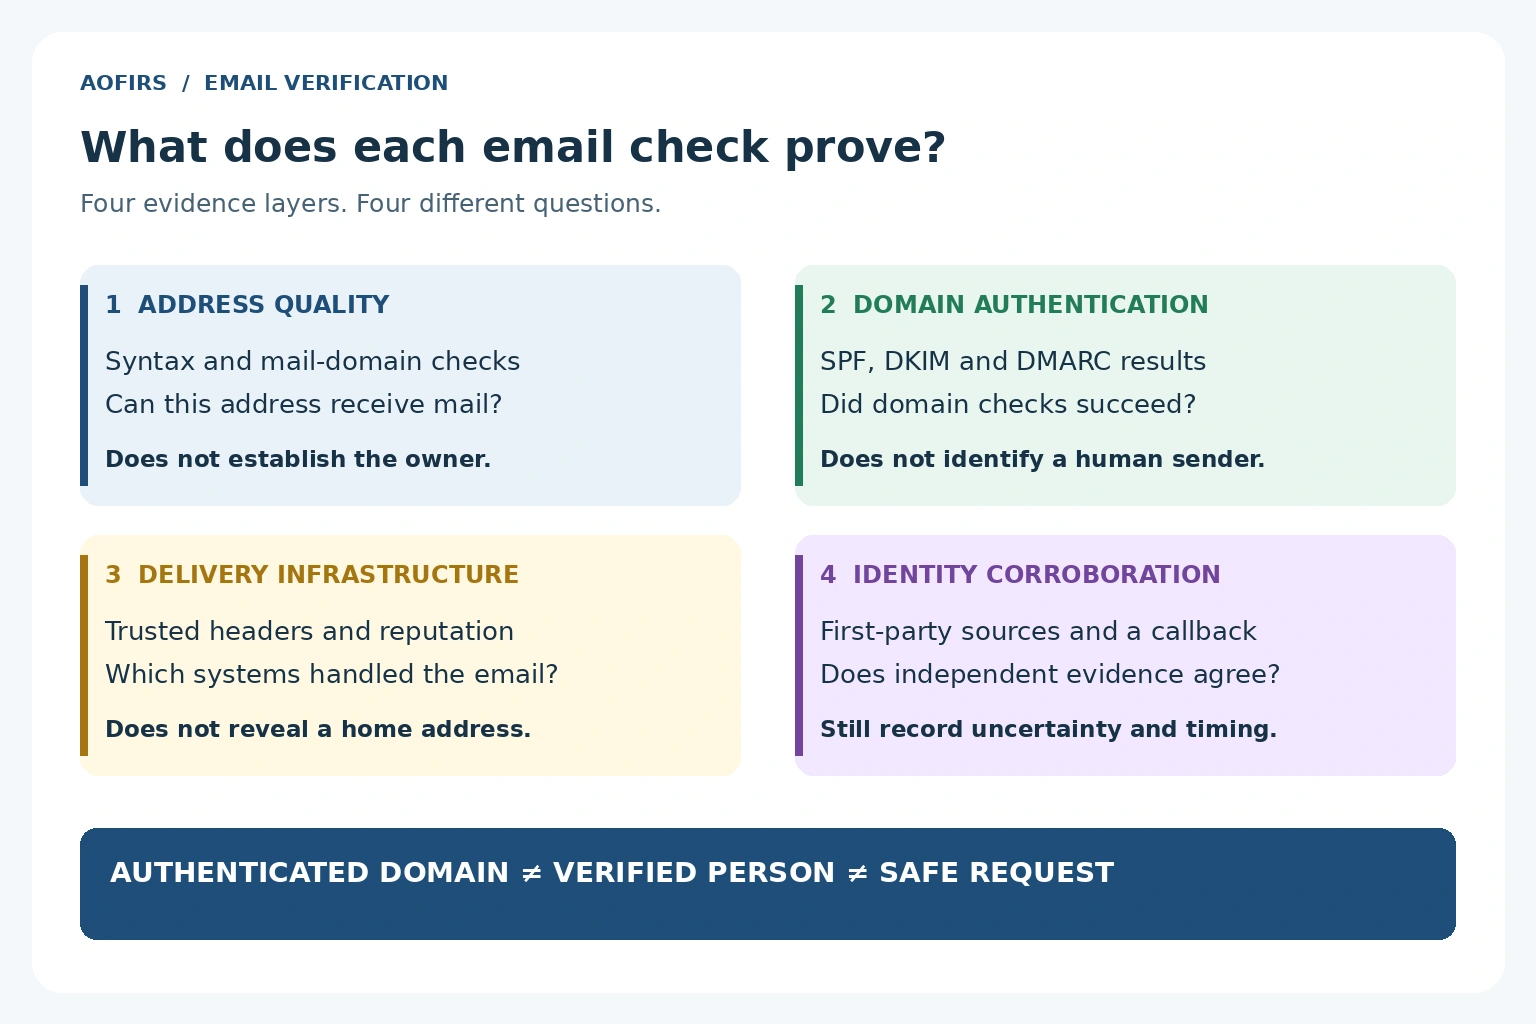
Researchers often use the same term for different jobs. Separating them prevents an address-quality report from becoming an unsupported statement about an individual.
Address quality
Check syntax, mail-domain configuration and available delivery signals.
Question: is this address likely to receive mail?
Domain authentication
Review the receiving system’s SPF, DKIM and DMARC findings.
Question: do the technical checks support the claimed sending domain?
Infrastructure analysis
Examine trusted routing records, timestamps and reputation evidence.
Question: what systems handled this message?
Identity corroboration
Compare exact-address associations with authoritative and independent sources.
Question: what supports the claimed person or organisation?
Why the “From” Field Is Only a Starting Point
A display name is easy to imitate. The visible address can also be misleading, whether through spoofing, a lookalike domain or an account that has been compromised. Expand the sender details and compare the complete domain with the organisation’s established address.
Check Reply-To as well. A different reply destination deserves an explanation, but it is not automatically fraudulent. Help desks, mailing systems and customer-service platforms may legitimately route replies elsewhere. The useful question is whether the difference fits the sender’s known workflow.
For public-source identity research, the AOFIRS reverse email lookup investigation guide explains how an exact email address can become a research lead. A public association, even on a plausible profile, does not prove current mailbox control or authorship of a particular message.
How to Read Full Headers Without Overstating the Evidence
Preserve the original message first
Keep the original message source or an available .eml export. A screenshot omits technical fields, and an ordinary forward may add another delivery chain or lose useful context. Record when you received the message and when you collected the evidence. Keep a separate working copy for annotations or redactions.
In desktop-browser Gmail, open the message, use the menu beside Reply and select Show original. Google documents this route in its full-header help guide. Other clients use labels such as message source, raw message or Internet headers; the exact menu depends on the client and version.
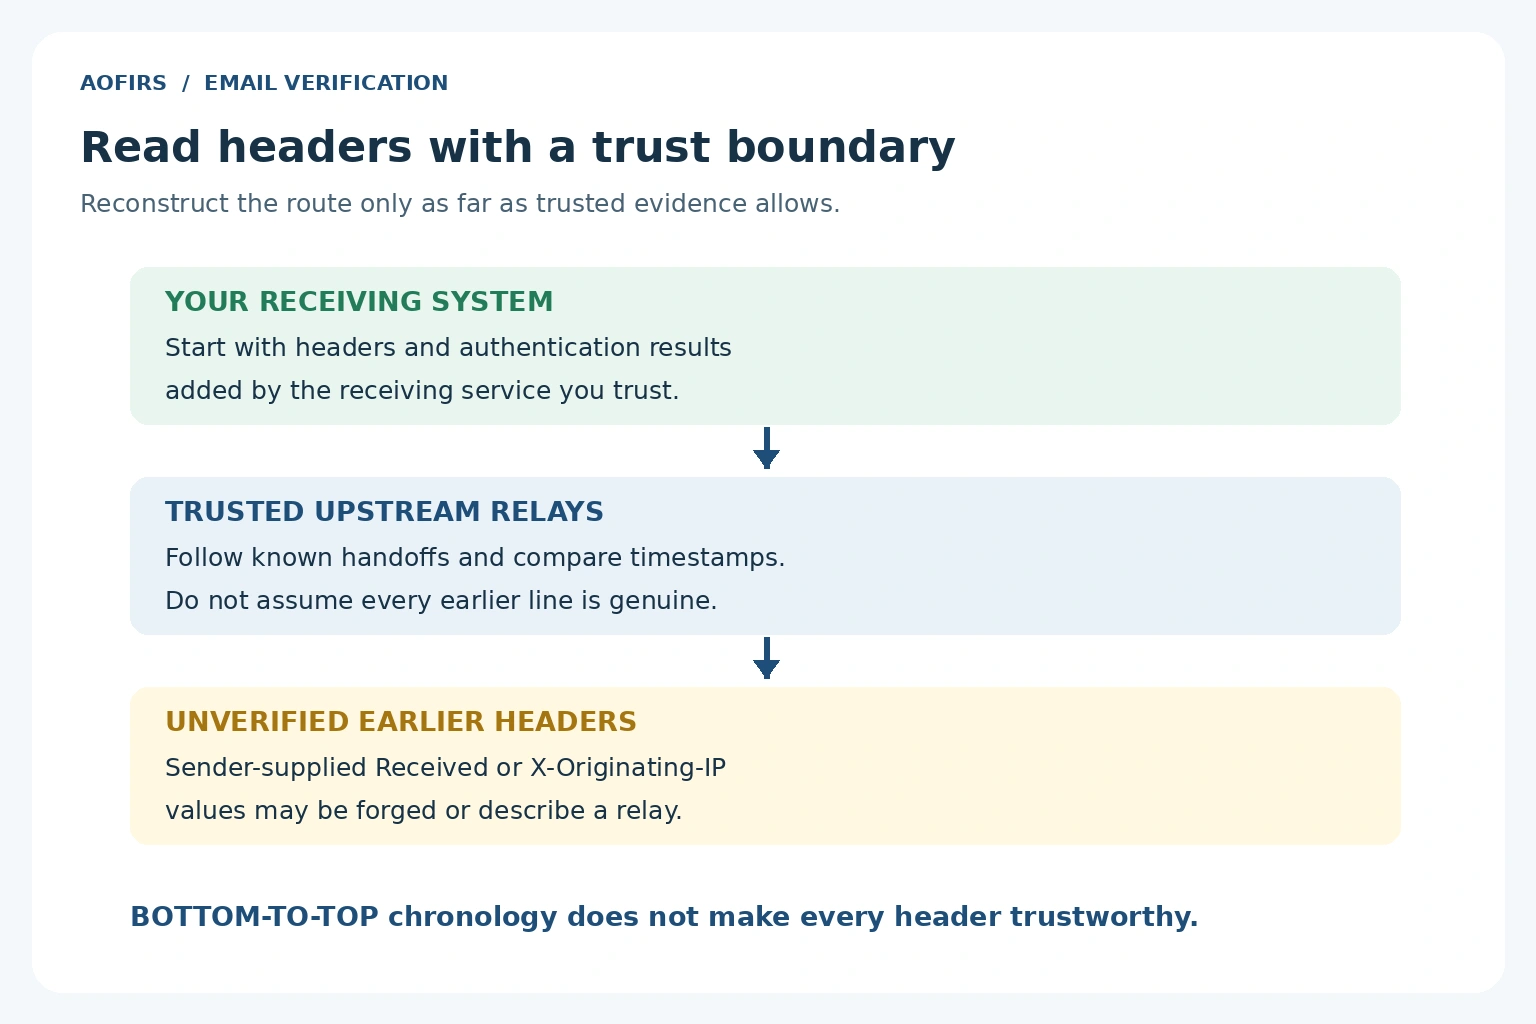
Identify the trust boundary before following the route
Receiving SMTP servers prepend Received records, as described in the SMTP specification. Reading valid entries from bottom to top can reconstruct chronology. However, the lowest entry is not automatically genuine, and earlier records supplied before the message reached trusted infrastructure can be fabricated.
Start by identifying the entry added by your receiving provider and the upstream connection it observed. Follow earlier handoffs only where their provenance is understood. A mail gateway, forwarding service or hosted provider may explain an apparently unexpected route. If the evidence stops at a relay, record that limit rather than naming it as the sender’s device.
The same discipline applies to Authentication-Results. The authentication-results specification explicitly considers forged fields. A copied line saying dmarc=pass has evidential value only when you know which system generated it and why that system is trusted.
What SPF, DKIM and DMARC Actually Establish
These mechanisms authenticate technical relationships involving domains. They do not certify the honesty of a message, identify an individual employee or rule out account compromise.
| Check | What it assesses | What to avoid concluding |
|---|---|---|
| SPF | Whether the connecting server is authorised for the checked SMTP envelope domain or HELO identity. | SPF does not by itself authenticate the visible From address or the human sender. |
| DKIM | Whether a signature validates against the signing domain’s published key for the covered message data. | The signing domain need not be the visible From domain. A valid signature does not make the request safe. |
| DMARC | Whether a passing SPF or DKIM result aligns with the visible From domain under the applicable alignment rules. | A pass is domain-level evidence. A compromised account or attacker-owned lookalike domain can still send authenticated mail. |
The SPF specification describes authorisation of sending hosts for SMTP identities. The DKIM specification describes signatures over selected message data. Read the domain identifiers alongside the pass or fail result; the result alone leaves out important context.
2026 standards update: RFC 9989, published in May 2026, replaces the older core DMARC specification. DMARC can pass through aligned SPF or aligned DKIM; it does not require both to pass. A published handling policy expresses the domain owner’s preference, while the receiving service applies its own handling decisions.
Forwarding and message modifications can affect authentication. A failure should prompt investigation of the route and configuration, rather than an automatic accusation of fraud. Equally, a pass should not override a suspicious request to change bank details, disclose credentials or bypass a normal approval process.
AOFIRS’s Forensic Guide to Email Verification in the AI Era provides a visual companion to these distinctions. Use it to connect authentication checks with the wider identity-verification process.
Historical Case: A Lottery Email and Conflicting Clues
The original AOFIRS/CIRS teaching example describes a lottery message using the name “Mrs. Maria Cook”, with a separate Gmail reply destination. Its headers reportedly included infrastructure associated with OCN and an X-Originating-IP value of 41.86.234.171.
Historical evidence only: the original lesson reported reputation, geolocation, blocklist and reverse-DNS findings. Those lookups have not been repeated for this update. They should not be described as the address’s present status.
The teaching value is the need to reconcile the message’s claim, reply destination and technical records. The IP field alone does not prove which device submitted the message, who used it or where that person lived. Its reliability depends on who inserted it and whether trusted observations corroborate it.
The old map result also does not establish a residential location. Geolocation is an estimate associated with network infrastructure, and a map visualisation is not an independent confirmation of its underlying dataset. Likewise, two reputation services may rely on overlapping feeds. Counting five tools is not the same as obtaining five independent sources.
When evidence repeats across databases, examine its origin, timestamp and scope. AOFIRS’s guide to verifying people-search results explains why duplicated or outdated associations need corroboration. Apply that same source-evaluation discipline to email infrastructure and identity findings.
What Verification and Investigation Tools Can Help With
Choose a tool by the question it answers. The categories below describe investigative roles, rather than a ranked buying list or a claim that one platform can establish a complete identity.
| Tool category | Useful output | Practical limitation |
|---|---|---|
| Address-quality services | Syntax, domain and available mailbox-deliverability signals. | Catch-all behaviour, temporary errors and anti-enumeration controls can produce uncertain results. |
| Professional email discovery | Possible addresses, patterns or public business associations. | An inferred address is a lead, not proof that a named individual controls it. |
| Header parsers | A clearer view of timestamps, relay sequence and authentication fields. | Parsing does not authenticate every input field or identify the human sender. |
| IP reputation and network lookups | Hosting operator, reported abuse and approximate geography. | A shared relay, VPN or compromised server may be unrelated to the sender’s physical location. |
| Licensed identity databases | Potential associations that can be compared with relevant primary records. | Access conditions, data quality and permitted uses vary. A match still needs corroboration. |
Mailbox checks commonly combine several signals. Mail servers may accept many recipient names, conceal whether a mailbox exists or reject checks temporarily. A service’s “deliverable” label is therefore an assessment of address quality, not a certificate of ownership. Record uncertain or catch-all findings as uncertain.
Protect the evidence when using online tools. Full headers can include private addresses and internal infrastructure details. Keep the original intact, use a redacted copy where appropriate, and check whether a third-party service is suitable before submitting it. The AOFIRS digital security guidance for researchers explains practical account and source-protection measures that support this work.
Why Convincing Language Is a Weak Authenticity Test
Generative AI can help produce polished text, but an investigator usually cannot establish from wording alone whether a particular email was AI-written. Grammar, tone and familiarity with a project are weak evidence of authenticity. They should not outweigh contradictory technical records or an unusual request.
A compromised account can expose genuine correspondence and enable a fraudulent message inside a familiar conversation. Such a message may use normal infrastructure and pass domain authentication. This is why independent confirmation of sensitive instructions remains necessary even when the headers appear routine.
AI can assist with explaining header fields or organising notes, provided the underlying evidence is checked. It should not invent missing hops, turn an IP estimate into a street address or convert a public association into a verified identity. Keep observations separate from interpretations.
An Eight-Step Email Verification Workflow
- Define the question. Separate address quality, message authentication and identity. State which claim or request needs verification.
- Preserve the original. Save the message source and record collection times. Work on a copy.
- Compare visible identifiers. Inspect the exact From domain, Reply-To and any claimed organisation. Note differences without treating every difference as fraud.
- Read trusted technical observations. Identify the receiving-system trust boundary and examine routing and timestamps within that boundary.
- Interpret authentication and alignment. Record SPF, DKIM and DMARC results, the domains tested and relevant routing explanations.
- Assess infrastructure evidence. Record what an IP represents, when reputation checks were performed and whether sources are independent.
- Corroborate identity and sensitive instructions. Use authoritative public associations and an independently obtained contact channel. Do not simply reply to the suspect address.
- Write a bounded conclusion. Explain what the evidence supports, what contradicts it, what remains unknown and the next action.
For supporting training material, AOFIRS’s research report on email verification and fraud prevention brings together email-source checking, header analysis and related learning resources. It complements the workflow without replacing a documented assessment of the actual message.
Example of a defensible conclusion
“The receiving provider reports a valid aligned DKIM signature and a DMARC pass for the visible sending domain. The message’s request to change payment details has not been independently confirmed. These checks support domain authentication, but do not establish who operated the account. Pause the payment change until the known supplier confirms through the established contact channel.”
The CIRS Research Principle
The original article draws on AOFIRS CIRS™ Training Module 9, Unit 23. Its enduring research lesson is to understand what a tool measures before relying on its result. Technical knowledge is useful when it helps distinguish observed facts, plausible explanations and unsupported assumptions.
For researchers, journalists and security professionals, a good assessment includes contradictions and unknowns. The absence of a blocklist entry is not proof of safety, and a polished message is not proof of identity. Evidence should support the specific conclusion being made.
Conclusion
Email verification works best as a sequence of questions, rather than a single pass-or-fail score. Address checks assess deliverability; authentication checks assess domain relationships; headers describe observed delivery events; independent sources and trusted contact channels help corroborate identity and intent.
Preserve the message, establish the trust boundary and document the limits of each finding. When a request carries consequences, confirm it independently before acting. The strongest conclusion is one that explains both what is supported and what still needs verification.
Frequently Asked Questions
1. Does a valid email address prove who owns it?
No. An address may be deliverable while shared, reassigned or compromised. Ownership or control requires separate evidence.
2. Does a DMARC pass mean an email is safe?
No. It supports aligned domain authentication. It does not prove the sender’s identity or the legitimacy of the message’s request.
3. Must both SPF and DKIM pass for DMARC to pass?
No. A passing result from either mechanism can satisfy DMARC when the authenticated domain aligns appropriately with the visible From domain.
4. Can full email headers be forged?
Some fields can be forged. Place confidence in observations added by trusted receiving systems and assess earlier entries according to their provenance.
5. Can an IP address reveal the sender’s exact location?
A lookup may indicate approximate network geography. It does not reliably identify a person’s home, device or physical location.
6. Is a different Reply-To address proof of phishing?
No. It is a clue to investigate. Legitimate mailing and support systems can use a different reply destination.
7. What is the safest way to verify new payment instructions?
Contact the organisation through an established, independently sourced channel and follow its normal approval process. Do not rely only on the email thread.
8. Should I upload full headers to an online analyser?
Check for private information and the service’s suitability first. Preserve an intact original and use a suitably redacted working copy when appropriate.
Sources and Review Scope
The technical links embedded above lead to Google’s header-access guidance and primary IETF documentation for SMTP, SPF, DKIM, DMARC and Authentication-Results. The historical case is drawn from the existing article’s CIRS teaching material and has not been presented as a new investigation.
Diagrams illustrate technical distinctions; the AI-generated laptop illustration is conceptual. None is a screenshot of a real message or evidence from the historical case.