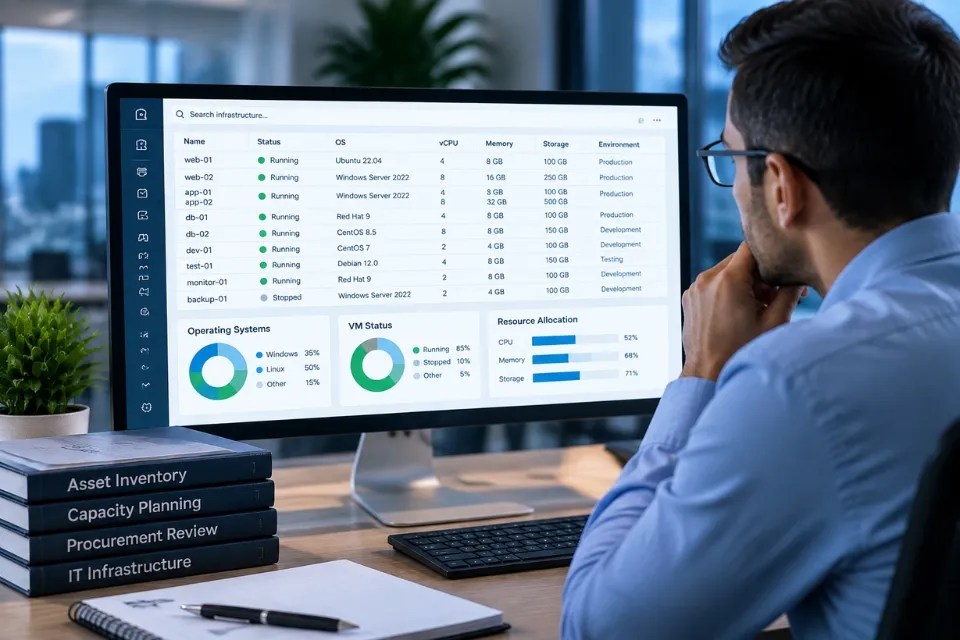
Cybersecurity research often starts outside an organization. Researchers examine domains, IP addresses, exposed services, public records, threat reports, and other accessible sources to identify potential risks. This evidence can reveal valuable clues, but it cannot show what occurred on an individual device.
Endpoint detection and response, commonly known as EDR, helps fill that gap. EDR tools collect endpoint activity that analysts can use to examine suspicious processes, connect related events, and reconstruct a sequence of actions.
Open-source EDR tools make this type of research more accessible. They allow security professionals to study endpoint behavior, test detection logic, and build practical investigation skills without relying entirely on a closed platform.
Why Endpoint Visibility Matters to Cybersecurity Research
External intelligence may indicate that a domain is suspicious or that a file hash appears in a threat report. It does not establish whether a device contacted the domain, whether the file ran, or what occurred next.
Endpoint telemetry provides that local context. Depending on the tool, operating system, and configuration, researchers may be able to examine process creation, file activity, network connections, registry changes on Windows systems, user sessions, and other system events.
This data helps investigators move beyond isolated indicators. Instead of asking only whether an indicator exists, they can ask more precise questions:
- Which device encountered it?
- Which process initiated the activity?
- Which user account was active?
- Did the process launch another process?
- Were files created, changed, or deleted?
- Did comparable activity appear elsewhere?
Recorded events can help researchers develop a timeline. Analysts must still interpret that timeline carefully because the presence of an event does not, by itself, prove malicious intent.
What Open-Source EDR Contributes to an Investigation
One of the main benefits of open-source software is that its source code is available for inspection. Subject to the project’s licensing terms and the expertise required to review the code, researchers can examine how the software collects and processes endpoint data.
They can also consult project documentation, review publicly documented development activity, examine detection rules, and learn from community contributions. The degree of transparency and supporting information varies by project, so each tool should be assessed individually.
Open-source EDR also supports controlled experimentation. A security team can deploy a tool in an isolated lab, observe how authorized test activity appears in endpoint data, and evaluate whether the available telemetry answers its research questions.
This flexibility can be useful for specialized projects. Teams may adapt queries, dashboards, or detection content to suit a particular environment. Students and newer practitioners can use the same tools to learn how endpoint events contribute to an investigation.
However, open source does not automatically mean easy to deploy, cost-free to operate, or appropriate for production. Its practical value depends on the project’s maturity, the deployment objective, and the resources available to maintain it.
Key Capabilities to Examine Before Selecting a Tool
An EDR project should be evaluated against the questions the researcher or security team needs to answer. A long feature list matters less than relevant and dependable telemetry.
Start with coverage. Identify which operating systems, endpoint types, and event categories the tool supports. A project may provide detailed data for one platform but limited information for another. Researchers should also determine whether the telemetry gives them enough context to connect users, processes, files, and network activity.
Next, assess the available detection functions. Some projects concentrate on data collection and investigation. Others include detection rules, behavioral analysis, alerts, or response controls. The right model depends on whether the intended use is research, continuous monitoring, incident response, or a combination of these functions.
The investigation workflow matters just as much as data collection. Analysts need practical ways to search events, filter noise, trace process relationships, and build timelines. Useful endpoint data becomes less valuable when the interface or query process makes analysis unnecessarily difficult.
Teams developing an initial shortlist may use resources such as Heimdal’s open source endpoint detection and response overview to identify tools for further investigation. Each option should then be assessed through its official documentation, source repository, licensing terms, supported platforms, and controlled testing.
Account for the Full Operational Cost
An open-source tool may not require a traditional license fee, but a production deployment still consumes resources. Organizations may need infrastructure, data storage, administrative time, security expertise, and an established maintenance process.
Endpoint monitoring can generate substantial event volumes, especially across a large or diverse device estate. Before deployment, teams should decide which events they need, how long to retain them, and whether the platform can search the resulting data efficiently.
Detection content also requires maintenance. A rule that performs well in one environment may produce excessive alerts in another because software, user activity, and administrative practices differ.
Teams need a process to review detections, document changes, manage false positives, and confirm that important activity remains visible. These demands do not make open-source EDR a poor option. They mean that an evaluation should account for infrastructure, staffing, expertise, and long-term ownership alongside acquisition cost.
Turn Endpoint Events into Defensible Findings
Collecting events is only the first step. Researchers need a repeatable method for turning telemetry into conclusions that others can examine and reproduce.
Begin with a defined question. An investigator might ask whether an endpoint contacted identified infrastructure, whether an unfamiliar application ran, or whether related activity appeared on several systems. A specific question helps determine which events are relevant.
Next, establish a timeline. Place recorded events in sequence and examine their relationships. A network connection may appear ordinary in isolation but warrant closer review when it follows an unexpected process launch or file modification.
Finally, separate observations from interpretations. A process start, connection, or file change may be directly recorded. The purpose behind it may remain uncertain. Good research states what the data confirms, identifies what the analyst has inferred, and notes what remains unresolved.
Place Open-Source EDR Within Layered Security
EDR provides evidence from endpoints, but endpoints are only one part of an organization’s technology environment. Relevant information may also reside in identity systems, email services, network controls, cloud platforms, vulnerability records, and external intelligence sources.
Open-source EDR should therefore serve a defined role within a broader security strategy. It may act as a research platform, a source of endpoint telemetry, a detection component, or part of a larger investigation workflow.
Teams must also plan what happens after an alert. An investigation may lead to containment, remediation, credential changes, access restrictions, or additional evidence collection. A tool’s response functions should be assessed separately from its visibility and detection features.
This distinction is important because detecting an event does not guarantee that an organization can contain or resolve it. Responsibilities, escalation paths, and response processes should be established before the tool becomes part of routine security operations.
Build a Practical EDR Evaluation Checklist
Before adopting a tool, researchers and security teams should document their requirements and test candidates in a controlled environment.
The checklist should cover:
- Supported operating systems and endpoint types
- Process, file, network, user, and platform-specific telemetry
- Data completeness and reliability
- Search, filtering, and timeline capabilities
- Detection-rule availability and customization
- Alert context and prioritization
- Storage and retention requirements
- Integration with existing security systems
- Available response and containment controls
- Documentation quality
- Source-code and repository availability
- Project update activity
- Community support
- Required administrative skills
- Expected maintenance workload
The final choice should reflect the intended use. A project suitable for research and education may not meet the availability, scalability, or support requirements of a production environment. Conversely, a complex platform may be unnecessary for a focused laboratory project.
From Experimentation to Sustainable Endpoint Visibility
Open-source EDR tools can help researchers examine activity that external intelligence alone cannot reveal. They provide endpoint evidence that may connect processes, files, network communications, users, and event sequences.
Their value depends on the quality of the questions asked, the relevance of the telemetry collected, and the care applied during interpretation. Teams also need realistic plans for deployment, storage, tuning, maintenance, and response.
The goal is not simply to collect more data. It is to create reliable endpoint visibility that helps researchers explain what happened, identify what remains uncertain, and make better-supported security decisions.